Service Mesh Architecture: A Guide to Microservices Communication
A company breaks its monolithic application into forty separate microservices, celebrates the architectural win, and then discovers a new problem nobody warned them about: every single service now needs to handle retries, encryption, authentication, and traffic routing on its own, with each team implementing this shared plumbing slightly differently.
A service mesh exists specifically to pull all of that scattered, duplicated logic into one consistent layer.
What a Service Mesh Actually Is
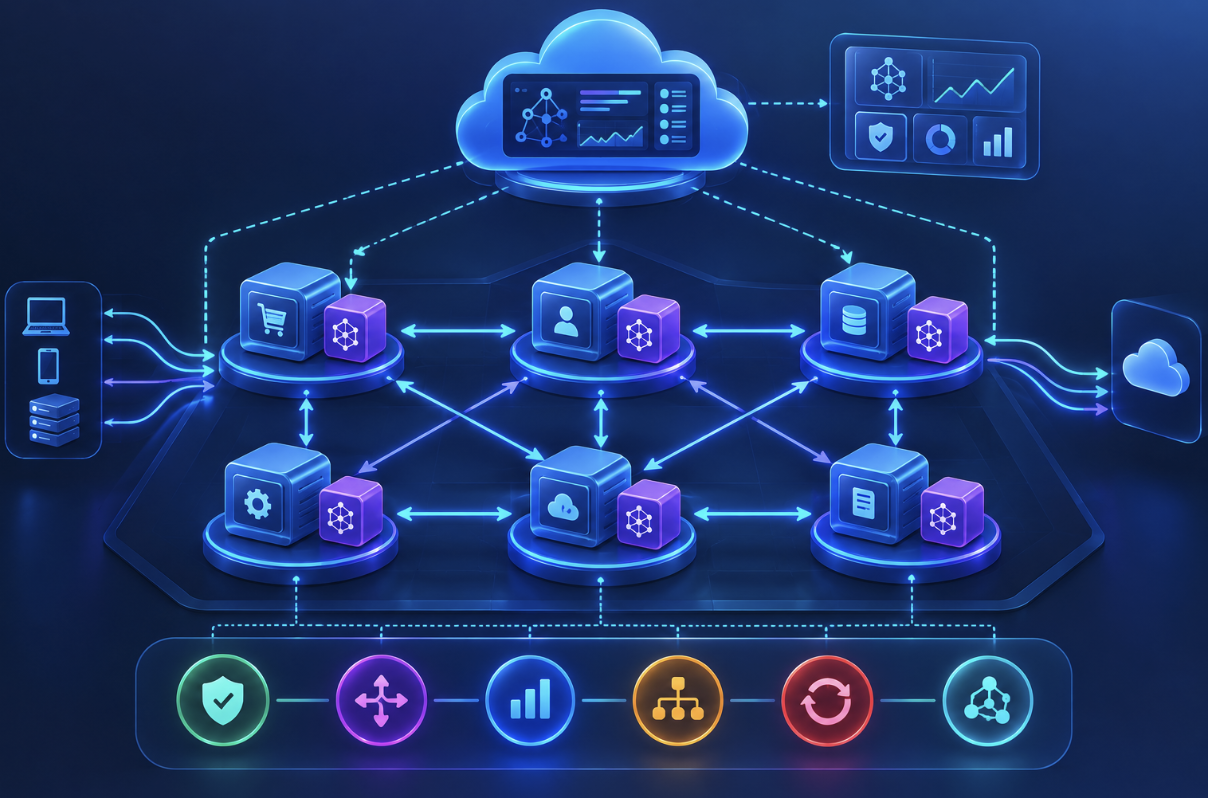
A service mesh is a dedicated infrastructure layer that handles communication between microservices, managing concerns like traffic routing, security, and observability without requiring individual services to implement this logic themselves. This typically works through lightweight proxies deployed alongside each service, intercepting and managing all the network traffic flowing in and out.
This infrastructure-layer approach means service-to-service communication concerns get handled consistently across an entire system, rather than each individual team reimplementing the same networking logic slightly differently within their own specific service, exactly the fragmentation our opening company ran into once they’d split into forty separate pieces.
Why Microservices Need This Kind of Shared Layer
Breaking a monolithic application into numerous microservices multiplies the network communication happening between components. Each service-to-service call now needs to handle failures, retries, and security considerations that simply didn’t exist within a single, unified application. This growing complexity is exactly what motivated the development of dedicated service mesh technology.
A monolithic application handles most function calls internally, within a single process, largely avoiding network-related failure modes entirely. Breaking that same functionality into separate microservices means what used to be a simple internal function call now travels across a network, introducing possibilities for failure, delay, and security exposure that a service mesh specifically exists to manage consistently.
The Technical Architecture Behind Service Mesh Implementation
Most service mesh implementations deploy a lightweight proxy alongside each individual service instance, commonly called a sidecar. These proxies intercept all network traffic to and from their associated service, applying policies around routing, security, and monitoring consistently. A separate control plane component manages and configures these distributed proxies across the entire system.
What a Service Mesh Actually Handles on Behalf of Services
Traffic management capabilities include load balancing, routing rules, and retry logic applied consistently across services. Security features handle encryption between services and enforce authentication policies. Observability capabilities provide consistent metrics, logging, and tracing across the entire distributed system without requiring each service to implement this instrumentation independently.
This consistency deserves particular emphasis, since before adopting a service mesh, each individual team within our opening company’s forty-service architecture would have needed to implement their own retry logic, their own encryption handling, and their own monitoring instrumentation, inevitably producing inconsistent implementations across different services that made troubleshooting and security auditing considerably harder than it needed to be.
Why Security Benefits From Centralized Service Mesh Management
Individual services no longer need to implement encryption and authentication logic independently. Centralized policy management makes it considerably easier to enforce consistent security requirements across an entire system. This centralization also makes rotating credentials or updating security policies considerably simpler than coordinating changes across numerous individual services separately.
How a Service Mesh Actually Improves System Observability
Consistent instrumentation across all services provides comprehensive visibility into system behavior. Teams can trace requests as they flow through numerous different services without each individual service needing custom tracing code. This consistent observability becomes increasingly valuable as the number of services within a system continues growing.
The Complexity and Overhead a Service Mesh Introduces
Implementing a service mesh adds additional infrastructure complexity to a system. The sidecar proxy pattern introduces some performance overhead for every single service-to-service communication. Organizations need real technical expertise to properly implement and maintain this additional infrastructure layer.
Teams new to service mesh technology sometimes underestimate the learning curve involved, since successfully operating this infrastructure requires understanding not just the mesh technology itself but also how it interacts with existing deployment and networking infrastructure, representing meaningful additional operational complexity beyond simply running the microservices themselves.
When a Service Mesh Makes Sense for an Organization
Organizations running numerous microservices with genuine, complex inter-service communication needs benefit considerably. Systems requiring consistent security and observability across many services see particular value. Smaller systems with just a handful of services often don’t need this additional infrastructure complexity, since the coordination problem a service mesh solves simply doesn’t reach meaningful scale yet.
What Our Opening Company Actually Gained From Adopting a Service Mesh
Once implemented, the forty separate teams no longer needed to individually solve retry logic, encryption, or monitoring, that shared responsibility moved into the mesh layer, letting each team focus on their own service’s actual business logic rather than reimplementing the same networking plumbing over and over.
Troubleshooting also became considerably easier, since every service now produced consistent tracing data through the same underlying infrastructure, rather than forty different teams’ forty different, inconsistent approaches to logging and monitoring.
Final Thoughts
A service mesh provides a valuable, dedicated infrastructure layer handling the shared communication concerns microservices architectures inevitably introduce, centralizing traffic management, security, and observability rather than requiring each service to solve these problems independently.
For that company staring down forty inconsistently implemented services, a service mesh is exactly the shared foundation that turned scattered duplication into something coherent.
Frequently Asked Questions
1. Do all microservices architectures need a service mesh?
No, smaller systems with limited service-to-service communication complexity may not benefit enough to justify the additional infrastructure overhead, with service mesh value scaling considerably with genuine system complexity and service count.
2. Does a service mesh slow down service-to-service communication?
The sidecar proxy pattern does introduce some performance overhead, though well-implemented service mesh technology generally keeps this overhead relatively modest for most typical use cases.
3. Is implementing a service mesh difficult for teams without prior experience?
This presents a learning curve, requiring understanding of both the specific mesh technology and how it integrates with existing infrastructure, making dedicated learning investment worthwhile before broader production adoption.
4. Can a service mesh replace the need for API gateways?
These generally serve different, complementary purposes, with API gateways typically managing external traffic entering a system, while service mesh technology manages internal service-to-service communication specifically.
5. Do all service mesh implementations use the same underlying technical approach?
No, various different service mesh technologies exist with somewhat different architectural approaches, though most share the general sidecar proxy pattern as their core underlying technical foundation.
6. Will service mesh adoption likely continue growing as microservices architectures become more common?
Yes, as organizations continue adopting microservices architectures at scale, the coordination challenges service mesh technology addresses become increasingly relevant, suggesting continued growing adoption.