How Confidential Computing Makes It Impossible to Steal Data Even While Processing
A server can process sensitive data without letting the cloud administrator see the data itself. Confidential computing changes that model by protecting data while it is being processed, not just while stored or moving across a network.
In this article, we will discuss how confidential computing technology ensures that data remains protected and cannot be stolen, even while it is being processed.
Your Data Is Most Exposed When It Is Actually Being Used
Most people think encryption solves the entire data-security problem. It does not. Encryption at rest protects stored files, while encryption in transit protects information moving between systems. During processing, applications traditionally need readable data in memory.
That creates a valuable target. If an attacker gains privileged access to a server, operating system, hypervisor, or debugging interface, sensitive information could potentially be exposed. Confidential computing addresses this gap with a hardware-based Trusted Execution Environment, or TEE.
Confidential Computing Creates a Protected Room Inside the Server
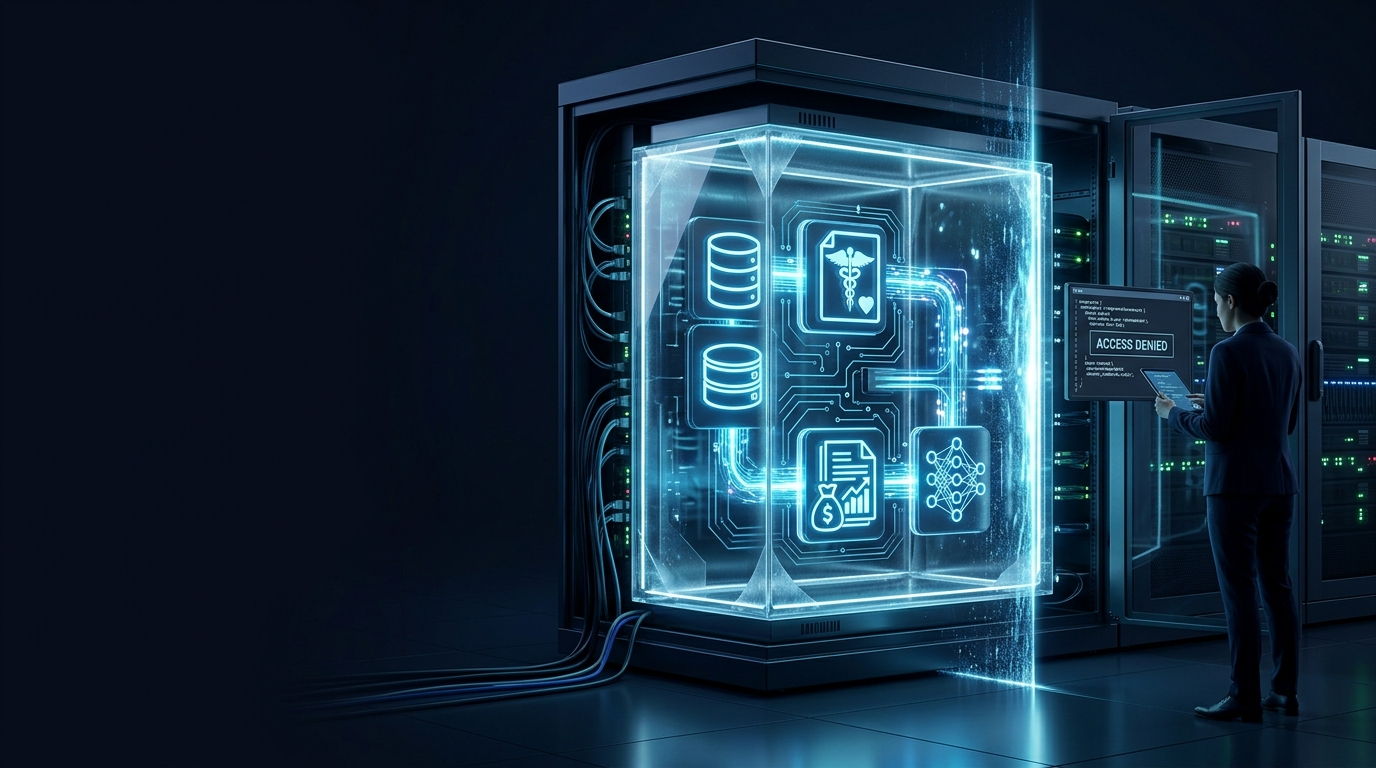
The key idea behind confidential computing is isolation. A TEE separates protected workloads from much of the surrounding system. Depending on the technology, this can mean an application enclave or an entire confidential virtual machine.
Inside the TEE, authorized code can work with sensitive information. Outside it, the data is protected from ordinary access. Intel SGX uses secure enclaves to isolate selected code and data, while AMD SEV protects confidential virtual machines using hardware-assisted memory encryption.
Why the hardware matters
Software-only isolation can depend heavily on the operating system and administrator privileges. Confidential computing moves a critical part of the trust boundary into hardware, reducing the infrastructure that must be trusted.
Attestation Stops the System From Trusting an Unknown Environment
Here is the part many basic explanations skip: confidential computing is not only about encryption. It is also about verification.
Before sensitive keys or data are released, an attestation process can provide evidence about the protected environment and software running inside it. A policy can then decide whether that environment meets the required conditions.
Attestation helps verify that a genuine TEE is present and correctly configured. Secure key release can then allow keys to be released only after the workload proves through attestation that it is running inside a trusted environment.
That creates a simple sequence:
- The workload starts inside a protected environment.
- The environment produces attestation evidence.
- A verifier checks the evidence.
- Approved keys are released.
- The application decrypts and processes the data inside the TEE.
The result is a much smaller window in which sensitive information can be exposed.
The Cloud Provider Does Not Automatically Get a View of Your Data
This is one of the biggest reasons confidential computing matters for cloud security. Organizations often hesitate to place sensitive workloads in public clouds because the provider operates parts of the underlying infrastructure.
Confidential computing is designed to reduce that trust requirement. Properly configured confidential environments can help prevent cloud operators, privileged administrators, and other software outside the TEE from accessing protected data while it is processed.
In my experience with clients, this distinction is easy to miss: moving encrypted data to the cloud is not the same as protecting it during computation. The processing layer needs its own security boundary. This matters when the workload runs on infrastructure you do not fully control. Especially when sensitive records or proprietary models are involved.
That matters for healthcare records, financial analysis, customer databases, intellectual property, and AI workloads where input data may be more sensitive than the final result.
Pro Tip: Do not treat confidential computing as a replacement for normal security. Keep encryption at rest, encryption in transit, identity controls, application security, logging, patching, and access management. Confidential computing adds protection to the data-in-use stage.
Confidential Computing Is Powerful, But It Does Not Make Theft Impossible
The technology is not magic. Confidential computing reduces specific attack paths; it does not eliminate every way data can be stolen.
The protected environment still depends on secure hardware, firmware, trusted software, correct configuration, strong key management, and sound application design. A vulnerability inside the trusted workload can still expose information. An application that sends sensitive data outside the TEE can defeat the purpose.
Organizations should start with a clear threat model. Map sensitive information from the moment it enters an application until the moment results leave the protected environment. This reveals where conventional controls stop and where confidential computing can add another boundary. Ask what you are protecting, who you do not want to trust, where keys are held, what code can access the data, and what evidence must be verified before processing begins.
Conclusion
Confidential computing can also support collaboration. For example, financial organizations can analyze shared fraud patterns without giving each other unrestricted access to raw customer information. It can also support sensitive AI and multiparty analytics where organizations need useful results without broadly exposing their underlying datasets.
Start today by identifying one workload containing sensitive information and map where that data is exposed during processing. Then ask: which part of that processing environment must be trusted?
FAQ’s
1. Is confidential computing the same as encryption?
No. Confidential computing focuses on protecting data while it is processed inside a hardware-based trusted environment. Encryption at rest protects stored data, while encryption in transit protects data moving between systems. A strong architecture can use all three protections together.
2. Can cloud administrators access confidential computing data?
Properly configured confidential computing is designed to prevent cloud operators and privileged software outside the trusted environment from accessing protected data during processing. Exact protection depends on the selected TEE, workload design, key controls, and platform configuration.
3. Does confidential computing prevent every data breach?
No. It reduces specific risks around data in use, but it cannot fix insecure applications, compromised trusted code, stolen credentials, poor key management, or intentional data leakage. Organizations should combine confidential computing with identity security, secure development, monitoring, patching, and other defensive controls.